I use the website anyns.io and found that I can set up DNSSEC, but when I try to configure it in my domain registrar's backend, it keeps showing a registry interface error. Does this mean it's impossible to set up DNSSEC? My domain has the .ad suffix.
N.HT
Join the discussion among hosting experts!

I think it's possible.
The main issue is that some providers' proxy interfaces prevent users from enabling DNSSEC directly in the management panel.
For example, my n.ht domain, which is a very niche domain from the Republic of Haiti. There are only about 2,000 registered globally. I'm even worried they might go out of business.
At my previous domestic registrar, I didn't see any function for DS settings, nor the ability to set glue records (which will be needed when anyns launches the custom ns record feature).
After I transferred the domain to netim, it worked. I just tested and DNSSEC can be enabled and verified successfully, which shows that the key is the proxy interface and maintenance capability of the registrar.
Also, at my previous domestic registrar, there was no way to hide whois info for .ht, but now netim directly supports whois privacy protection.
You're using .ad, which is also niche, but its registration volume is many times that of .ht. I suggest finding a more reputable and larger provider.
SIGN还在折腾技术的老登!
I have my .ad at DYNADOT. I feel like their company is pretty big now, and they also have DNS settings functionality, but I just can't set it up. It keeps showing a registry interface error.
Well, anyns.io itself is also on dynadot, and I have no problem submitting DS records. Of course, .io is a generic TLD.
Generate a DS record in the anyns backend
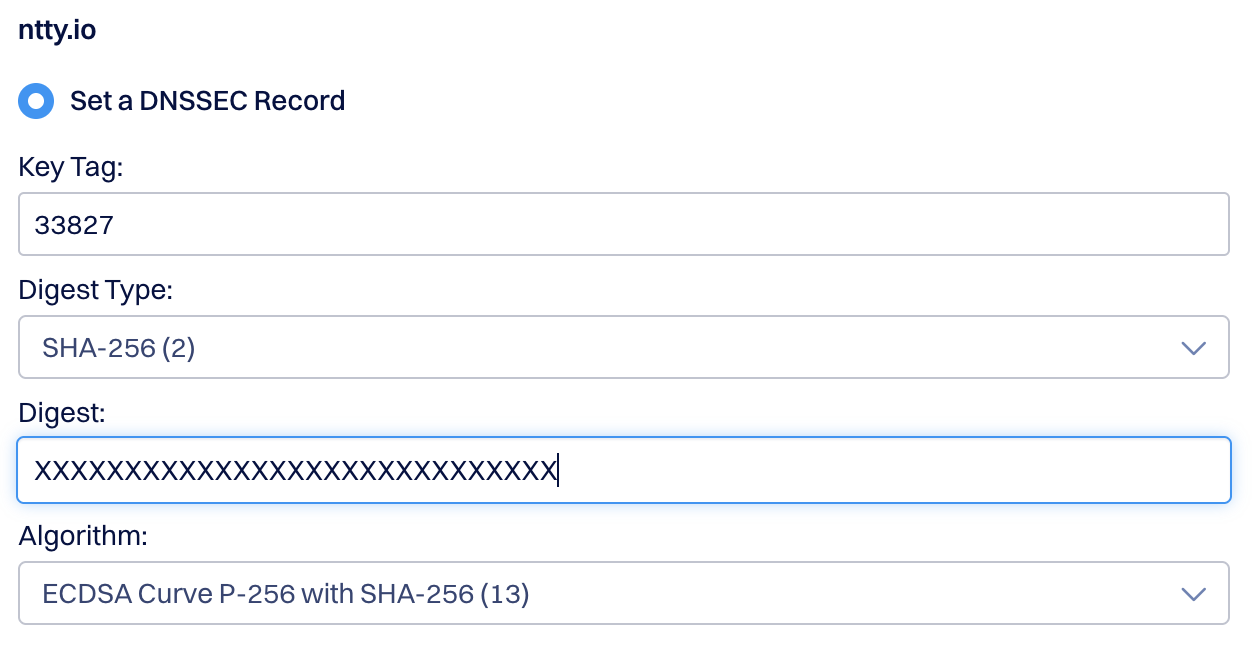
ntty.io. 3600 IN DS 33827 13 2 XXXXXXXXXXXXXXX
When submitting to the registry, it looks like this:
If it still doesn't work, you'll have to contact customer service.
SIGN还在折腾技术的老登!
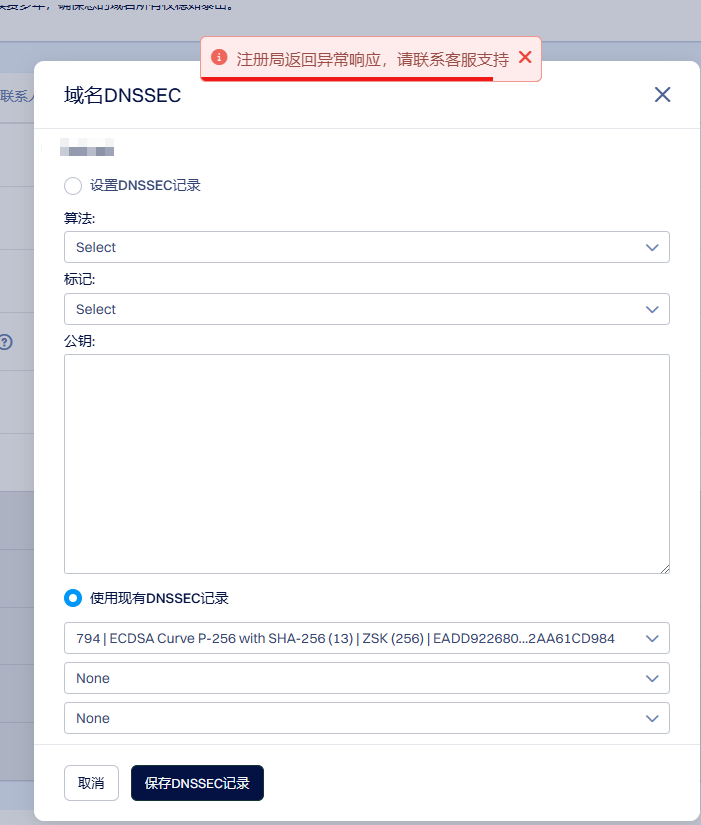
Mine looks like this, the .ad domain. I didn't notice it before, just submitted a ticket.

code
$ dig DS ad +short
6062 8 2 3C07A798097F38D173D98194F436A2ED29443ECC1DA0D9F8DA8ABFA2 9348D6CE
The .ad domain can have DNSSEC set up.
If it really doesn't work, just switch providers. Of course, I'm not saying dynadot is bad. It's just that supporting DNSSEC for these country-code domains may indeed have some technical or policy limitations. The specifics still depend on the registry and the provider's support.
If Shoushou (the expert) says it's supported, then maybe it is—Showfom is still an authority in the Chinese domain name community.
SIGN还在折腾技术的老登!
Login